📊 Full opportunity report: Tailscale Ops Find SQLite WAL Corruption Cause on IdeaNavigator AI — validation score, market gap, and execution plan.

Get business pricing on tech for your team
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
TL;DR

An IdeaNavigator AI item describes Tailscale tracing database corruption to a SQLite write-ahead-log reset bug dating back 16 years. The brief supplies no technical account, affected versions, impact details or fix, so the reported cause and its practical implications cannot be independently assessed from the available information.
IdeaNavigator AI has flagged a report that Tailscale traced database corruption to a SQLite write-ahead-log reset bug dating back 16 years, a development that could matter to security and operations teams using software that relies on SQLite. The brief does not identify affected Tailscale components or versions, describe the corruption, or say whether a fix is available, so the technical scope remains unconfirmed here.
The item is presented under the headline “Tailscale Traces Database Corruption to 16y/o SQLite WAL-Reset Bug.” It characterizes the issue as a cause identified by Tailscale, but supplies no engineering post, incident timeline, affected database files, reproduction details, or statement from the company. The reported attribution and age of the bug therefore cannot be checked against technical documentation in the brief.
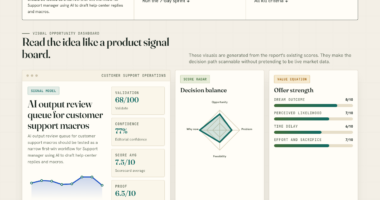
The material is primarily a product opportunity proposal, not an incident report. It suggests a monitoring service that watches Hacker News and similar feeds, filters emerging security developments for security leads at small and mid-sized organizations, and produces short summaries of what changed, why it matters and what action might follow. It says Hacker News surfaced this item with an 88/100 signal, without defining the scoring method, scale, or comparison baseline.
The proposal recommends testing the service by delivering this brief and two other security items to five people in the target role and tracking whether a recipient changes a decision or forwards the item. That is a suggested validation plan, not evidence of customer demand or demonstrated business results. No subscription price, user feedback, or operational outcomes are reported.
Tailscale Ops Find SQLite WAL Corruption Cause
IdeaNavigator AI reports that Tailscale linked database corruption to an old SQLite WAL-reset bug. The brief lacks technical details needed to confirm the cause or determine who may be affected.
What the brief reports
The reported link is between database corruption and SQLite write-ahead logging behavior.
Cause identified
IdeaNavigator AI attributes the finding to Tailscale, but provides no engineering account to verify it.
Scope is unknown
No affected products, versions, configurations, or database files are named.
What operators can conclude
The brief does not establish customer impact or a security incident.
- Database corruption is reported.
- The alleged cause involves an old SQLite WAL-reset bug.
- Whether data was lost, exposed, or recovered.
- Whether any customer system was affected.
What the signal service proposes
The concept aims to help smaller security teams spot and assess emerging reports.
Collect emerging security items from Hacker News and similar sources.
Share this item and two others with five people in the target role.
See whether a brief changes a decision or is forwarded. No pilot results are reported.
Evidence gaps to close
A headline and an unexplained score are not enough to guide an affected organization.
| Question | Available detail |
|---|---|
| Affected systems? | No product, component, version, or configuration identified. |
| Fix or mitigation? | No remediation guidance provided. |
| Score meaning? | 88/100 method and comparison baseline are unexplained. |
Why the Report Could Matter to Operators
If the reported connection is accurate, an old database edge case could have current consequences when software depends on SQLite’s write-ahead logging (WAL) behavior. Corruption can affect the reliability of stored data, but the brief does not establish what information was affected, whether any customer systems were exposed, or whether the event created a security risk. Those distinctions matter: database corruption is not by itself evidence of a breach or data loss.
The monitoring concept addresses a practical information problem for smaller security teams: relevant disclosures may appear in technical forums before they reach formal advisories or an organization’s usual reporting channels. A concise, role-specific alert could help teams decide whether to investigate. But a useful alert needs a verifiable link to the underlying report, clear confidence levels, and actionable guidance; a headline and an unexplained score cannot establish that an organization is affected.
Products Worth Considering

Amazon Kindle Scribe Colorsoft 64GB with Premium Pen

Bose QuietComfort Wireless Noise Cancelling Headphones, Sandstone

Kindle Paperwhite Signature Edition 32GB (2024 Model) – Metallic Black
As an affiliate, we earn on qualifying purchases.
The Proposed Security Signal Monitor
IdeaNavigator AI frames the Tailscale item as an example for a cybersecurity operations signal monitor. The proposed service would collect emerging threats and disclosures from Hacker News and other feeds, then prioritize material for security leads at smaller organizations rather than provide a general news roundup. The stated business model is a subscription, but the brief offers no pricing or evidence that the service has launched.
The proposal’s suggested first test is narrow: send three briefs, including this item, to five people matching the target role within a week, then see whether anyone changes a decision or shares a brief with a colleague. That test would provide an early indication of usefulness, though five recipients would not establish broad demand. The document does not report that the test has taken place.
What the Incident Brief Leaves Open
The available details do not establish which Tailscale product or component experienced corruption, when the issue occurred, what SQLite version or configuration was involved, or whether the reported bug has a public identifier. The brief also does not say whether data was lost, recovered, exposed, or affected beyond a particular system. It provides no company statement, technical write-up, vulnerability advisory, or remediation instructions.
It is also unclear what “16y/o” refers to: the age of the underlying SQLite behavior, the age of a known bug report, or another chronology. The 88/100 signal has no stated methodology, and there is no evidence in the brief that the proposed monitoring product has been built, that its pilot has run, or that prospective users have validated its value.
Verification and Pilot Remain Pending
The next technical milestone would be a detailed account from Tailscale or another directly attributable technical record identifying the affected systems, cause, scope, and any fix or mitigation. Until such information is available, organizations should not infer that their own systems are affected from the headline alone. The brief does not provide a recommended patch, workaround, or advisory to follow.
For the proposed monitor, the next step described is to deliver three briefs to five security leads and measure whether the information affects a decision or is forwarded. No results or launch date are given. The stated source for the underlying item is the IdeaNavigator AI page: IdeaNavigator AI.
Source: IdeaNavigator AI
Key Questions
What is the reported Tailscale development?
IdeaNavigator AI describes a report that Tailscale traced database corruption to a SQLite WAL-reset bug said to date back 16 years. The brief does not include a technical report confirming the details.
Which Tailscale products or versions are affected?
The brief does not identify any affected product, component, version, or configuration. The scope cannot be determined from the information provided.
Does the report confirm a security breach or data loss?
No. It refers to database corruption but gives no details about data loss, exposure, or unauthorized access. Corruption alone does not establish that a breach occurred.
What is the 88/100 score?
IdeaNavigator AI says Hacker News surfaced the item with an 88/100 signal. It does not explain the score’s method, scale, or comparison baseline, so it should not be treated as a measure of incident severity.
Has the proposed monitoring service been tested?
The brief proposes sending three security briefs to five people in the target role and tracking whether they affect decisions or are shared. It does not say that this test has happened or report any results.
Source: IdeaNavigator AI