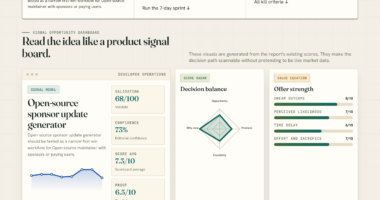
📊 Full opportunity report: Best Tools For Checking Device Security In Remote Teams on IdeaNavigator AI — validation score, market gap, and execution plan.
Play games included with Prime
Start a Prime free trial and play with Amazon Luna on your devices.
Start playingAs an affiliate, we earn on qualifying purchases.
TL;DR

A new lightweight device security checker is emerging for remote teams with mixed hardware, helping companies verify encryption, updates, and security posture without invasive management. This addresses compliance gaps for SMBs facing SOC 2 and customer security reviews.
A new lightweight device security checker designed specifically for remote teams with mixed hardware is in the early stages of deployment. This tool aims to verify device encryption, OS updates, screen lock status, and password manager presence, providing a compliance report without remote control capabilities. The development responds to increasing security and compliance demands for SMBs managing employee-owned devices across different operating systems. See how AI benchmarks are being used in security.
The proposed solution is a voluntary, installable agent that checks core security features on employee devices, including disk encryption, OS patch levels, and screen lock activation. It reports the device’s security posture to a centralized dashboard, where teams can view compliance status and receive self-remediation instructions. The tool is designed to address the verification gap left by traditional Mobile Device Management (MDM) solutions, which are often too invasive for employee-owned hardware.
According to an anonymous source familiar with the project, the initial deployment targets ten remote startups that are preparing for SOC 2 audits and customer security reviews. The goal is to measure device enrollment rates and assess whether auditors accept the generated reports as sufficient evidence of security posture. Learn more about national security tools. The tool’s revenue model involves per-device monthly pricing and exporting compliance reports on a paid tier.
This approach is seen as a potential first step in a broader market for SMB endpoint security, offering a lightweight, non-invasive alternative to traditional management solutions that often face resistance from employees and small organizations.
Implications for SMB Security Compliance
This development addresses a significant gap in the security management of employee-owned devices in remote teams, especially for SMBs facing increasing regulatory and customer security requirements. By providing a lightweight, voluntary verification tool, companies can improve their security posture documentation without the invasiveness of full MDM solutions. This can streamline compliance processes like SOC 2, reduce risk of breaches, and enhance trust with clients and auditors.
Moreover, as remote work persists and device diversity grows, such tools could become essential for maintaining security standards across a broad and varied hardware landscape. The ability to verify device security status quickly and accurately can also reduce the time and cost associated with compliance audits, making security management more accessible for smaller organizations.
device security checker for remote teams
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Growing Need for Remote Device Security Verification
The rise of remote work has led to a proliferation of employee-owned devices accessing corporate data, creating new security challenges. Traditional Mobile Device Management (MDM) solutions, which are often used to enforce security policies, tend to be invasive and are not well-suited for personal devices. As a result, many companies face a verification gap during compliance audits, with no reliable way to confirm device security status without intrusive measures.
Recent regulatory pressures, such as SOC 2 and customer security reviews, have increased the demand for proof of secure device configurations. Meanwhile, the market for endpoint security tools tailored for small and medium-sized businesses (SMBs) is expanding rapidly, with an emphasis on lightweight, easy-to-deploy solutions. This context has driven interest in minimal agents that can perform security checks without disrupting employee privacy or workflow.
Previous attempts at remote device management have focused on full control solutions, but these are often too invasive for employee-owned hardware. The emerging approach is to develop lightweight, voluntary checkers that provide compliance evidence while respecting user autonomy.
lightweight endpoint security verification tool
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Uncertainties About Adoption and Auditor Acceptance
It is not yet clear how quickly companies will adopt this new device checker at scale or whether auditors will accept the generated reports as sufficient evidence of security posture. The success of the initial deployment at ten startups will be a key indicator, but broader acceptance remains uncertain. Additionally, questions remain about the tool’s effectiveness across different OS versions, device types, and in diverse security environments.
Further testing is needed to determine if the reports meet regulatory standards and how they compare to traditional management solutions in terms of reliability and comprehensiveness.
employee device encryption verification software
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Next Steps for Deployment and Validation
The initial deployment at ten startups will provide valuable data on device enrollment rates, compliance levels, and auditor acceptance. If successful, plans include scaling the deployment to more organizations and refining the reporting features based on user feedback. Ongoing validation will focus on ensuring the tool’s reports align with regulatory expectations and provide actionable insights.
Further development may involve integrating self-remediation capabilities or expanding device checks to include additional security features. The project team also aims to establish partnerships with compliance auditors to formalize acceptance criteria for the reports.
OS update compliance tool for remote devices
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Key Questions
How does the device security checker work?
The tool is a voluntary agent installed on employee devices that checks for disk encryption, OS updates, screen lock activation, and password manager presence. It reports the security status to a dashboard without remote control or invasive management.
Will this tool replace traditional MDM solutions?
No, it is designed as a lightweight supplement for verification purposes, especially suited for employee-owned devices where full management is impractical or invasive.
Is the tool compliant with privacy regulations?
Since it performs only security posture checks without remote control or data collection beyond security status, it aims to respect user privacy, but full compliance will depend on implementation and jurisdiction.
When will this tool be available broadly?
The initial deployment is ongoing, with broader availability contingent on successful validation and auditor acceptance. No specific launch date has been announced yet.
What are the costs associated with the tool?
The pricing model involves per-device monthly fees, with additional charges for exporting compliance reports on a paid tier.
Source: IdeaNavigator AI
NFL season / tailgating Picks
team gear
As an affiliate, we earn on qualifying purchases.